
Information Security Policy
Information Security Basic Policy
To appropriately protect our customers' and our own information assets, we have established a basic policy on information security and will continuously implement organizational and technical security management measures.
1. Purpose
We protect information assets from risks such as information leakage, alteration, loss, and unauthorized access, maintaining an environment where you can use our services with peace of mind.
2. Scope of application
This policy applies to the information assets handled by our company (personal information, order information, payment-related information, business information, systems and networks), as well as to our officers, employees and contractors.
3. Management system
- We will appoint a person in charge of information security and establish a management system.
- We will establish rules and procedures and clarify authority and responsibilities.
- Regular inspections and reviews will be carried out.
4. Risk Management
We assess risks based on the importance of information assets, prioritize them, and implement countermeasures accordingly. We review these measures as needed in light of environmental changes and new threats.
5. Technical and physical safety control measures
- Access rights management, strengthening authentication, and eliminating unnecessary accounts
- Log acquisition and maintenance, monitoring, vulnerability information collection and response
- Backup and recovery procedures
- Malware prevention, device and media management
6. Education and Awareness-raising
We will inform our executives and employees of the importance of information security and provide necessary education and awareness-raising on an ongoing basis.
7. Contractor management
When outsourcing tasks or using cloud services, we will verify the security management measures of the outsourcing partner and require appropriate management through contracts, etc.
8. Incident Response
We will establish a reporting and communication system in the event of an accident, and promptly investigate the cause, prevent further damage, and take measures to prevent recurrence. We will report and notify relevant organizations as necessary.
9. Compliance with laws and regulations
We will comply with the Personal Information Protection Act, other related laws and regulations, guidelines, and contractual obligations.
10. Continuous improvement
We will continuously improve our management system and safety control measures based on the results of audits and inspections, changes in the environment, and technological trends.
Key points on this page
- Declaration of protection of information assets and continuous improvement
- Clarifying management system, contractors, and incident response
- Clarifying contact points for inquiries
Contact Us
Choose from popular products
- Go to product details for CBX CORE Premium VAPE liquid.
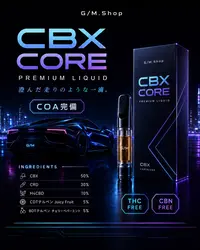
- CBX CORE Premium VAPE Liquid
- ¥7,920 ~ ¥15,180
- Go to product details for MamaWako (H4CBH(k) 70% CBX 10%) VAPE liquid.

- MamaWako (H4CBH(k) 70% CBX 10%) VAPE Liquid
- ¥8,800 ~ ¥22,330
- Go to product details for MDMA × MM Analog [For Research Use]
- MDMA × MM Analog [For Research Use]
- ¥12,100
- HHBD 60% VAPE Liquid product details
- HHBD 60% VAPE liquid
- ¥8,690 ~ ¥18,040